You signed in with another tab or window. Reload to refresh your session.You signed out in another tab or window. Reload to refresh your session.You switched accounts on another tab or window. Reload to refresh your session.Dismiss alert
{{ message }}
Repository navigation
fix(web): show saved service access with Local environment off - #26464
With Local environment off, the desktop app showed "No environment selected" in Sharing & access even while connected to a background service. The page now selects a connected service and offers a picker when several are available. Pairing and T3 Connect actions use that service's credentials and permissions. Desktop network controls remain restricted to the backend the app manages, and switching services clears the displayed pairing credential.
Verified head d86991209bf586bf1d152e6f1ae3590198f5750c, built from base a185dd924889cd7f925760431a9f29b973a35e2f. The rebase preserves main's new collapsed pairing-link preview. An independent Codex review found no findings.
Before
Historical Linux desktop reproduction at 48a292364ab37574c67fb377b5227e5d281d9203: a connected saved service has no access target with Local environment off.
linux-before.mp4
After at this head
Physical corex, Linux Electron 44.10.1, two real bundled servers on loopback ports 27731 and 27732 with separate test homes. Both services were enrolled through Add environment. Electron used the production gnome_libsecret backend with a task-isolated GNOME secret-service session collection. The saved connection catalog was encrypted; Electron's basic store was not used.
The recording follows Labs to Sharing & access, creates A's pairing link while Authorized clients is collapsed, switches to B, creates and revokes B's link, then returns to A. A's link survives B's revocation and its copyable credential is cleared on switching. It then revokes A's link, links A and B for publishing, unlinks A while B remains linked, and finally unlinks B. The last view shows Local environment off and both services connected. Idle pauses are shortened and the fixture boundary is captioned.
linux-final-short.mp4
Only unavailable external boundaries were fixtures: Clerk FAPI/session responses and its account widget, plus a local HTTPS relay. The real Clerk SDK, production renderer/hooks/controllers, selected-service HTTP authentication, and real /api/connect handlers ran unchanged. The relay fixture verified real Ed25519 proofs before returning invented per-environment credentials. The fixture certificate required Electron's --ignore-certificate-errors.
Cloud linking in the recording is publish-only. The managed T3 Connect switch is visible and stays off. After each action, authenticated reads of both real servers and hashes of their secret files confirmed the selected service changed and the other service did not. All five checkpoints passed.
The Browser panel also exercised primary-environment pairing creation and revocation at this head. The collapsed list displayed its new preview, then removed it on revocation.
Web and macOS/Windows desktop run the same ConnectionsSettings, AuthorizedClientsSettings, useCloudLinkController and executeConnectedEnvironmentHttpRequest paths exercised here. Native mobile has separate UI; no mobile call sites use the new pairing commands, and no native mobile UI changed.
Real server proof and checks
Against the two current-head servers, commands verified manual and managed link-proof signatures and claims, exact loopback ports, unauthorized/wrong-port rejection, account-mismatch rejection without mutation, and relay-config persistence. After restarting both servers, exact secret bytes, 0600 modes, preferences and signing keys survived. A's bearer failed on B; unlinking A left B's state and files unchanged.
Boat job j_kz4jyhrkvej3ewyhzgfy exited 0. vp run check:changed passed format, lint, both knip passes, affected-package typechecks, all 67 focused tests in 8 files, and 15 selected React compiler cases. vp run build:desktop passed. The focused run includes environment HTTP authentication, auth commands, saved-service credentials, cloud controller behavior, selection, pairing rows and scheduled-task compatibility.
Commands and successful output as text
PR #26464 current-head verification
Head: d86991209bf586bf1d152e6f1ae3590198f5750c
Build/test base: a185dd924889cd7f925760431a9f29b973a35e2f
Machine: physical corex, Linux, Electron 44.10.1
Build: Boat j_kz4jyhrkvej3ewyhzgfy, worker bx_3grjdm9s, large, attempt 1, exit 0
Build command: vp i --frozen-lockfile; vp run check:changed "$FLEET_SOURCE_BASE"; export T3CODE_CLERK_PUBLISHABLE_KEY=pk_test_Y2xlcmsuZml4dHVyZS50ZXN0JA; export T3CODE_CLERK_JWT_TEMPLATE=fixture-relay; export T3CODE_RELAY_URL=https://127.0.0.1:27740; vp run build:desktop
Runtime archive SHA256: 64c03516bf48ab18f9c91d5e9a0932f175d6de1069ea59b4e21f463542756ff7

The exact built desktop/server/web outputs were extracted without source edits.
Two real bundled server processes, separate test homes and ports 27731/27732:
node runtime/apps/server/dist/bin.mjs serve --base-dir /tmp/t3code-26464-rebase/service-a --port 27731 --host 127.0.0.1 --no-browser
node runtime/apps/server/dist/bin.mjs serve --base-dir /tmp/t3code-26464-rebase/service-b --port 27732 --host 127.0.0.1 --no-browser

Electron used --password-store=gnome-libsecret with a task-isolated D-Bus GNOME secret-service session collection.
Actual startup output: backend: gnome_libsecret
Persisted connection-catalog.json has only version and encryptedCatalog fields, 3584 bytes.
Both services enrolled through normal Add environment host/code UI. Local environment was off.

Native recording: Labs -> Sharing & access, selected A Create link with collapsed list -> new preview + Copy code; switch B -> A preview clears; create/revoke B; return A -> A link remains, credential cleared; revoke A; publish-only link A; link B; unlink A; return B still publishing; unlink B; Environments shows Local off and both connected.
Production client hooks/controllers/auth and real /api/connect handlers were unchanged.
Only external Clerk FAPI/session/account-widget and HTTPS relay responses were fixtures.
Real Clerk SDK, real server Ed25519 proofs verified at the relay fixture, invented per-service credentials.
Managed Connect switch stayed off. Publish-only linking/unlinking was exercised.
Video contains actual Electron viewport only, pauses shortened while retaining the setup and dialog and a fixture caption added.

Real-server proof commands:
node real-server-proof.mjs prepare proof-input-final.private.json
Stop/restart each captured server PID with the same base directory and port.
node real-server-proof.mjs verify-after-restart proof-input-final.private.json
Private input has only isolated loopback server credentials and is not attached.

A: GET /api/connect/link-state -> 200
A: POST /api/connect/link-proof -> 200
A: verified manual link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
A: POST /api/connect/link-proof -> 200
A: verified cloudflare_tunnel link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
A: POST /api/connect/link-proof -> 400
A: POST /api/connect/link-proof -> 401
A: POST /api/connect/relay-config -> 200
A: POST /api/connect/preferences -> 200
A: GET /api/connect/link-state -> 200
A: POST /api/connect/relay-config -> 409
A: real relay-config and preference handlers persisted six private secret files; exact values and 0600 modes verified; account mismatch rejected without mutation
B: GET /api/connect/link-state -> 200
B: POST /api/connect/link-proof -> 200
B: verified manual link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
B: POST /api/connect/link-proof -> 200
B: verified cloudflare_tunnel link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
B: POST /api/connect/link-proof -> 400
B: POST /api/connect/link-proof -> 401
B: POST /api/connect/relay-config -> 200
B: POST /api/connect/preferences -> 200
B: GET /api/connect/link-state -> 200
B: POST /api/connect/relay-config -> 409
B: real relay-config and preference handlers persisted six private secret files; exact values and 0600 modes verified; account mismatch rejected without mutation
A: GET /api/connect/link-state -> 401
B: GET /api/connect/link-state -> 401
PREPARE PASS. Stop/restart both isolated servers using their original base directories and ports, then run verify-after-restart with this same input file. No server, relay or process was mocked by this script.

A: GET /api/connect/link-state -> 200
A: POST /api/connect/link-proof -> 200
A: verified manual link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
A: restart retained linked state, publishing preference, exact relay-config secret bytes and signing key
B: GET /api/connect/link-state -> 200
B: POST /api/connect/link-proof -> 200
B: verified manual link-proof signature against persisted public key; challenge, environment, endpoint, loopback port, audience, TTL and scopes match
B: restart retained linked state, publishing preference, exact relay-config secret bytes and signing key
B: GET /api/connect/link-state -> 200
A: POST /api/connect/unlink -> 200
A: GET /api/connect/link-state -> 200
B: GET /api/connect/link-state -> 200
A: unlink removed only A's relay secrets; B's real link state and persisted bytes are unchanged
B: POST /api/connect/unlink -> 200
B: GET /api/connect/link-state -> 200
B: unlink removed B's relay secrets
VERIFY-AFTER-RESTART PASS. Real production HTTP auth, link-proof signing, configuration persistence, restart reads and selected-server unlink isolation verified. External Clerk/relay/tunnel/guest-link behavior remains unverified.

Cloud UI checkpoints:
baseline PASS: http://127.0.0.1:27731 linked=false publishing=false; http://127.0.0.1:27732 linked=false publishing=false; other service state and persisted file hashes unchanged.
link-a PASS: http://127.0.0.1:27731 linked=true publishing=true; http://127.0.0.1:27732 linked=false publishing=false; other service state and persisted file hashes unchanged.
link-b PASS: http://127.0.0.1:27731 linked=true publishing=true; http://127.0.0.1:27732 linked=true publishing=true; other service state and persisted file hashes unchanged.
unlink-a PASS: http://127.0.0.1:27731 linked=false publishing=false; http://127.0.0.1:27732 linked=true publishing=true; other service state and persisted file hashes unchanged.
unlink-b PASS: http://127.0.0.1:27731 linked=false publishing=false; http://127.0.0.1:27732 linked=false publishing=false; other service state and persisted file hashes unchanged.

Browser panel: same head primary pairing creation/revocation and collapsed preview passed.

Unverified: production Clerk login, live relay provisioning/revocation, managed connector startup, tunnel reachability and guest links through a live tunnel. No test account is available.

PR #26464 | head d86991209bf586bf1d152e6f1ae3590198f5750c
Base a185dd924889cd7f925760431a9f29b973a35e2f
Boat j_kz4jyhrkvej3ewyhzgfy | large bx_3grjdm9s | attempt 1 | exit 0
Command: vp i --frozen-lockfile; vp run check:changed "$FLEET_SOURCE_BASE"; vp run build:desktop

> vp test (8 files)  pass  21.4s

 RUN  v5.0.5 /tmp/fleet-job/j_kz4jyhrkvej3ewyhzgfy/src

 ✓  @t3tools/web (unit)  src/components/settings/ConnectionsSettings.logic.test.ts (17 tests) 5ms
 ✓  @t3tools/web (browser) (chromium)  src/components/settings/AuthorizedClientsSettings.browser.test.tsx (2 tests) 111ms
 ✓  @t3tools/client-runtime  src/state/auth.test.ts (2 tests) 3ms
 ✓  @t3tools/web (browser) (chromium)  src/cloud/useCloudLinkController.browser.test.tsx (8 tests) 196ms
stdout | unknown test
[02:00:03.182] WARN (#38): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
stdout | src/components/settings/ScheduledTasksSettings.browser.test.tsx > ScheduledTasksSettings > creates on a permitted secondary and reacts to permission changes
[02:00:03.286] WARN (#87): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
 ✓  @t3tools/client-runtime  src/state/environmentHttpAuth.test.ts (31 tests) 103ms
 ✓  @t3tools/web (unit)  src/cloud/linkEnvironment.test.ts (1 test) 41ms
stdout | src/components/settings/ScheduledTasksSettings.browser.test.tsx > ScheduledTasksSettings > keeps the permitted representative as the creation target
[02:00:03.534] WARN (#173): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
 ✓  @t3tools/web (browser) (chromium)  src/components/settings/ScheduledTasksSettings.browser.test.tsx (5 tests) 717ms
   ✓ ScheduledTasksSettings (5)
     ✓ creates on a permitted secondary and reacts to permission changes 319ms
stdout | unknown test
[02:00:06.200] WARN (#38): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
stdout | unknown test
[02:00:06.565] WARN (#173): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
stdout | unknown test
[02:00:09.232] WARN (#38): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
stdout | unknown test
[02:00:09.587] WARN (#173): Could not discover the primary environment. {
  error: [ConnectionTransientError: Remote environment endpoint returned an invalid response from http://localhost:62601/.well-known/t3/environment.],
}
 ✓  t3  src/provider/AgentContextBudget.test.ts (1 test) 75ms

 Test Files  8 passed (8)
      Tests  67 passed (67)
   Start at  01:59:52
   Duration  17.86s (transform 57%, import 20%, worker 16%, setup 5%, tests 2%)

> vp react compiler (15 files)  pass  7.5s

 RUN  v5.0.5 /tmp/fleet-job/j_kz4jyhrkvej3ewyhzgfy/src

 ✓  @t3tools/web (unit)  src/reactCompilerCoverage.test.ts (1305 tests | 1290 skipped) 137ms

 Test Files  1 passed (1)
      Tests  15 passed | 1290 skipped (1305)
   Start at  02:00:12
   Duration  5.94s (transform 66%, setup 25%, import 6%, tests 3%)

check:changed summary
  pass  unused patches  17.8s
  pass  format  0.2s
  pass  lint  0.7s
  pass  knip 1/2  5.8s
  pass  knip 2/2  12.5s
  pass  typecheck (40 packages)  27.6s
  pass  test (8 files)  21.4s
  pass  react compiler (15 files)  7.5s
  CI also runs: full test suites, build, rust, release smoke
  pass not cached: files changed during the run

Desktop build output:
✔ Build complete in 965ms

---
vp run: 5/5 successful. (Run `vp run --last-details` for full details)
Ready check compared this head with live main d51bc58f5e05123a416a3737ac4bce42d1d76b7c. The merge is clean. Main advanced after the build with #30389, which changes tool-output display and provider adapters. It does not touch access, pairing, authentication or cloud-link code; the current-head runtime evidence and checks still cover the final PR diff. Maria merged the base during verification. The resulting diff changes deployment tooling and dialog-title line height; access, auth, pairing and cloud operations are unchanged from the independently reviewed rebase. Tests, server proof and the client capture were rerun on the merged head. All required checks pass and no review threads are unresolved. Auto-merge is off and there is no merge queue entry.
Unverified live path: production Clerk login, live relay provisioning/revocation, managed connector startup, tunnel reachability, and guest links through a live tunnel. No dedicated test account is available. These external paths are not claimed by the fixture proof. Initial linking retains the server's existing loopback-origin restriction.
Implemented and rebased by Claude Opus 5.5 in Claude Code. Investigated, tested and independently reviewed by GPT-6.1 Sol in Codex through T3 Code.
Macroscope's review found this PR approvable — Access settings can now manage saved environments with Local environment off, using each environment's own authenticated connection. Access changes remain explicit and permission-scoped, while desktop backend controls stay restricted to the primary environment.
No code changes detected at d869912. Prior analysis still applies.
You can add or adjust custom eligibility rules. Learn more.
It looks like this branch is under active development. To avoid overwhelming you with review comments due to an influx of new commits, CodeRabbit has automatically paused this review. You can configure this behavior by changing the reviews.auto_review.auto_pause_after_reviewed_commits setting.
No actionable comments were generated in the recent review.
Walkthrough
Access settings can select an environment and use its session, permissions, and authentication commands. Cloud-link state and operations use the selected environment’s connected HTTP services. The changes also add tests and remote-access documentation.
Changes: Environment-scoped access and cloud links
The client runtime adds authenticated HTTP requests and pairing or client-management commands for connected environments. The primary-environment pairing, revocation, and session-state helpers are removed. Session state accepts a nullable environment ID.
Environment-scoped cloud-link state and operations apps/web/src/cloud/cloudLinkState.ts, apps/web/src/cloud/linkEnvironment.ts, apps/web/src/cloud/linkEnvironmentAtoms.ts, apps/web/src/cloud/primaryCloudLinkState.ts, apps/web/src/cloud/linkEnvironment.test.ts
Cloud-link reads and mutations use a target environment’s prepared connection. State, refresh, and cached reads are scoped to an environment. Tests check target-specific origins and bearer tokens.
Access settings resolve a selected environment and use its session state, permissions, and authentication commands. Pairing and client revocation target that environment. The documentation describes selecting an environment and managing a same-machine background service.
sequenceDiagram
  actor User
  participant ConnectionsSettings
  participant useEnvironmentSessionState
  participant authEnvironmentCommand
  participant ConnectedEnvironment
  User->>ConnectionsSettings: Select an environment
  ConnectionsSettings->>useEnvironmentSessionState: Read session for selected environment
  ConnectionsSettings->>authEnvironmentCommand: Create pairing credential or revoke client
  authEnvironmentCommand->>ConnectedEnvironment: Send authenticated request
  ConnectedEnvironment-->>authEnvironmentCommand: Return command result
Loading
Suggested reviewers:maria-rcks
Merge Risk: Minimal · up to d2bc9
The change lets Sharing & access work for a connected service when Local environment is off. No blocking risk was found in the reviewed changes. Signed-in T3 Connect and multi-environment selection were not exercised by the author. The T3 Connect onboarding dialog still acts on the primary environment; it behaved that way before this change.
Pre-merge checks: 4
Check name
Status
Explanation
Title check
The title is concise, conventional, and accurately describes the main change: showing saved-service access when Local environment is off.
Linked Issues check
Issue #26420 is the only active directly linked target. Its coding requirement: Settings → Sharing & access must show a connected non-primary service when Local environment is off. The page must offer…
Out of Scope Changes check
The whole-PR summary (merge base d897d3f to head d2bc956) shows changes that serve #26420: - Environment selection and picker in ConnectionsSettings and resolveAccessEnvironmentId. - Environment-s…
Description check
The description is comprehensive and relevant. It explains the problem and change, links issue #26420, provides extensive verification evidence, includes UI evidence, records limitations, and identifi…
Full details: Linked Issues check
Explanation
Issue #26420 is the only active directly linked target. Its coding requirement: Settings → Sharing & access must show a connected non-primary service when Local environment is off. The page must offer that service's settings and T3 Connect link/unlink controls, not 'No environment selected'.
Evidence at head d2bc956 (whole PR, merge base d897d3f):
resolveAccessEnvironmentId in ConnectionsSettings.logic.ts keeps a listed explicit selection. Otherwise it uses the listed primary environment, then a connected listed environment, then the first listed environment. It returns null only when no environments exist. ConnectionsSettings.tsx offers a picker when several are listed.
Access queries, session state, scopes, pairing, client revocation and cloud-link rows target the selected environment. SavedEnvironmentRows.tsx gives CloudLinkRow an environmentId, so the T3 Connect row renders for the selected service.
Cloud-link requests in linkEnvironment.ts and environment-scoped commands in packages/client-runtime/src/state/auth.ts run through the selected environment's prepared connection (executeConnectedEnvironmentHttpRequest).
The rebase adds managed-policy checks that follow the selected service. AuthorizedClientsSettings.browser.test.tsx (read at head) covers the selected service denying remote clients (pairing disabled) and an unmanaged selected service with a managed primary (pairing enabled). This matches the PR description.
Unproven at head: signed-in T3 Connect link/unlink and guest-link creation through a live tunnel. The issue requires the UI path and environment-scoped requests, and the code provides both. Live tunnel behavior does not change this verdict. Maria's run covers saved-service access and pairing on head 286d53a. It does not cover the later rebase at d2bc956.
Full details: Out of Scope Changes check
Explanation
The whole-PR summary (merge base d897d3f to head d2bc956) shows changes that serve #26420:
Environment selection and picker in ConnectionsSettings and resolveAccessEnvironmentId.
Environment-scoped cloud-link state, controller and commands (cloudLinkState.ts, linkEnvironment.ts, linkEnvironmentAtoms.ts, useCloudLinkController.ts, SavedEnvironmentRows.tsx, ConnectOnboardingDialog.tsx passing the primary ID).
Environment-scoped pairing and revocation in packages/client-runtime/src/state/auth.ts and environmentHttpAuth.ts. These replace primary-only helpers removed from apps/web/src/environments/primary/auth.ts, index.ts and sessionState.ts.
AuthorizedClientsSettings.tsx changes: selected-environment pairing and managed-policy checks for that environment. The rebase moved policy checks from the primary to the selected service, which is part of making pairing for the selected service correct.
Primary-only desktop network, Tailscale, WSL and onboarding controls keep the primary target. The PR description and summary state this, and it matches the issue's scope.
Comment, import and docs updates (SettingsScopeSentence.tsx, useAvailableSettingsSearchItems.ts, ScheduledTasksSettings.tsx, docs/user/remote-access.md, the environmentHttpAuth package export) and tests for the changed behavior.
The summary shows no server, server-authorization or native mobile changes. The rebase over PR #27197 did not add a file that the summary lists as unrelated. The server typecheck issue in AgentSessionScanner.ts, if present, is a main-branch condition and not a change of this PR.
Full details: Description check
Explanation
The description is comprehensive and relevant. It explains the problem and change, links issue #26420, provides extensive verification evidence, includes UI evidence, records limitations, and identifies the implementation tools. It does not use the template’s section headings and does not include an explicit maintainer approval comment, but the required information is otherwise substantially covered.
Finishing Touches
Generate docstrings
Commit to this branch
Create a new PR
Generate unit tests (beta)
Commit to this branch
Create a new PR
Autofix · Keep fixing CodeRabbit findings and required CI, and resolving merge conflicts
Included review availability: This review used your included allowance. Your plan provides up to 10 included reviews per hour; 8 remain after this review.
Verified head 286d53a8f18ce56c9a431d0ed7bec0f79c4ec711 on a Linux Boat VM. Reproduced on github/main (8b74a69019): real Electron with Local environment off and a connected saved service showed "No environment selected" in Sharing & access. On this PR, the same saved connection shows Permissions, Authorized clients, and Create link.
Used the real dev server, Electron renderer, and repository Playwright with system Chrome. Added a real git project through the app and ran Codex gpt-6.1-sol turns on both revisions. Both read README.md through a terminal; the PR returned PR_RUNTIME_OK. No mocks or injected desktop bridge.
Created a pairing code from saved-service access, paired a fresh Chrome client, then revoked it. The client lost its connection and returned to pairing on reload. Also created/revoked an unused link and verified primary web pairing creation/revocation. Desktop-only network controls remain absent for the saved service.
Actual saved-service requests, credentials omitted:
POST http://127.0.0.1:16733/api/auth/pairing-token -> 200 bearer=true
POST http://127.0.0.1:16733/api/auth/pairing-links/revoke -> 200 bearer=true
vp run check:changed 85bd3f2a2a0ad4a8ddf2950e01db80765e9a1bf4 passed through blacksmith-check: 39 package typechecks, 65 tests across 7 files, 15 selected React compiler checks, format, lint, both knip passes, and unused patches. No code changes.
Not verified
Signed-in T3 Connect linking/unlinking, managed tunnels, and guest links require an external test account that was unavailable. Multi-environment selection was not exercised because this pass used one server. macOS, Windows, native iOS and Android were not exercised on this Linux VM.
Merge verification, 2026-11-04
Merged current main (a185dd924889) without conflicts and pushed merge commit d86991209bf586bf1d152e6f1ae3590198f5750c to this head. No feature code changed. The PR diff remains 25 files, +852/-509.
All 33 GitCafe check contexts passed; GitHub reports CLEAN and MERGEABLE. Two independent scoped code reviews found no blocker or should-fix findings. No actionable bot threads were present.
Ran vp run check:changed a185dd924889cd7f925760431a9f29b973a35e2f through blacksmith-check: format, lint, both knip passes, unused patches, 40 package typechecks, 67 tests in 8 files, and 15 selected React compiler checks passed. Worker setup needed parent history and Playwright Chromium, then the complete check passed.
Fresh real Chrome pairing and the primary Sharing & access page worked on the merged head. Real Electron launched with Local environment off. Repeating saved-service pairing was blocked by unavailable desktop secure storage; using the configured protected backend opened a keyring prompt, so verification stopped without interacting with that prompt. The earlier saved-service evidence above is from the stated earlier head and is not a fresh runtime verification of this merge commit. Signed-in T3 Connect and the other platforms remain unverified.
…nvironment is off

With Local environment off there is no primary environment, so Sharing &
access showed "No environment selected" even while a background service on
the same machine was connected, and there was no way to link it to T3 Connect.

The page now picks an environment: the primary when there is one, otherwise a
connected saved environment, with a picker when several are connected.
Access changes, pairing links, revocations, session permissions and the
T3 Connect link all run on that environment with this client's own
credentials for it, through the shared authenticated environment HTTP helper.
Desktop network, Tailscale and WSL controls still appear only for the
desktop-managed local environment.

Co-Authored-By: Claude Opus 5.5 <noreply@anthropic.com>
This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
size:XXL1,000+ changed lines (additions + deletions).vouch:trustedPR author is trusted by repo permissions or the VOUCHED list.
2 participants
Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.


 github-actions
Bot
added
vouch:trusted


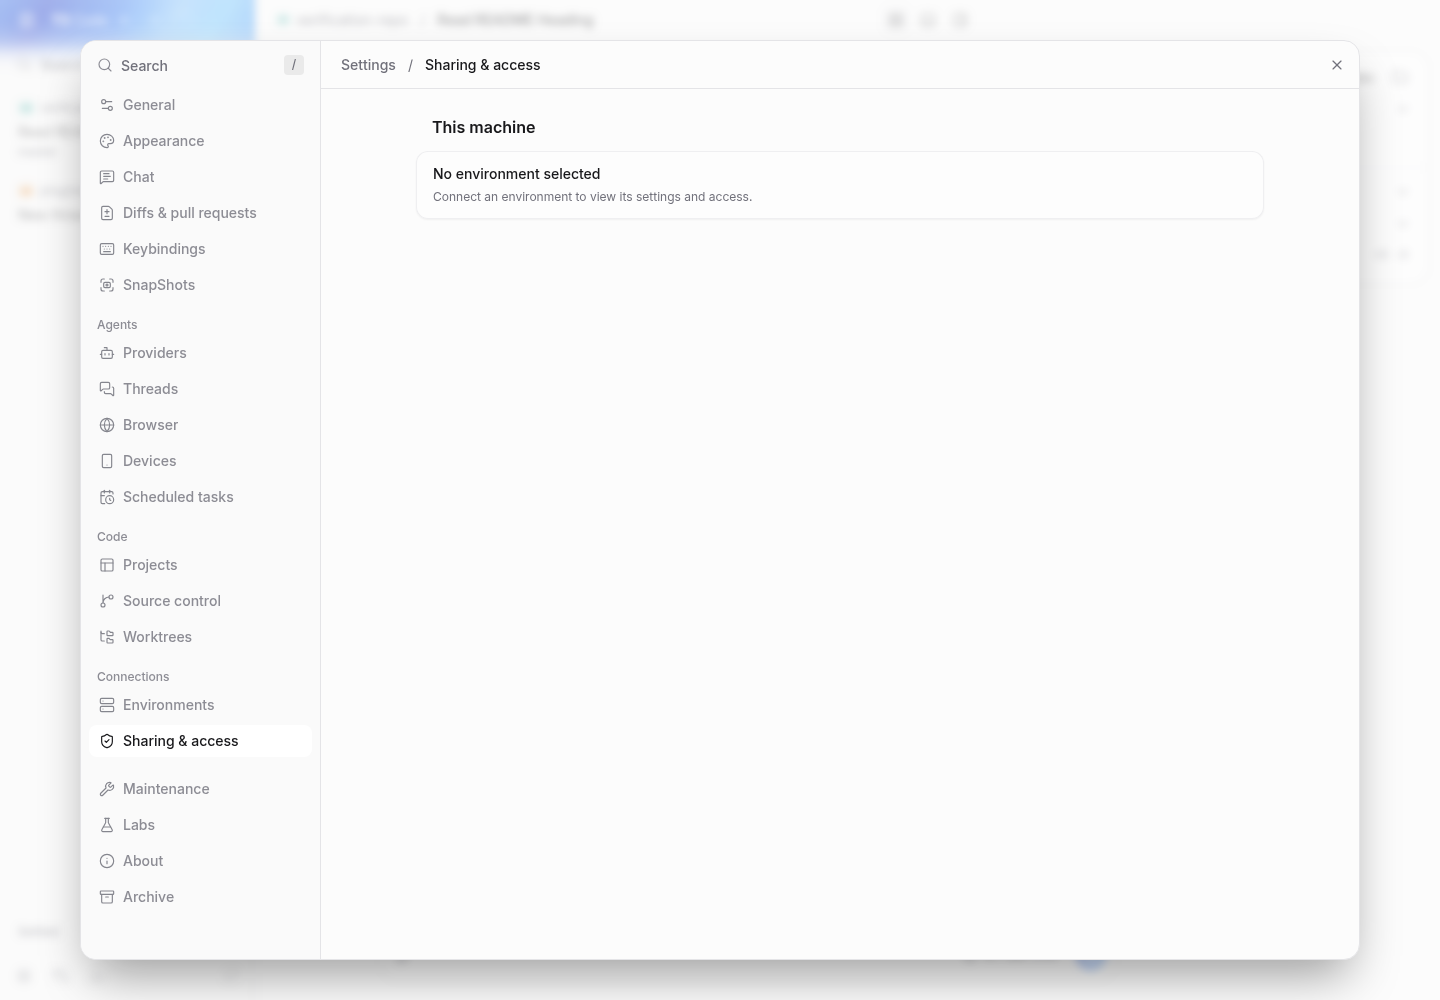
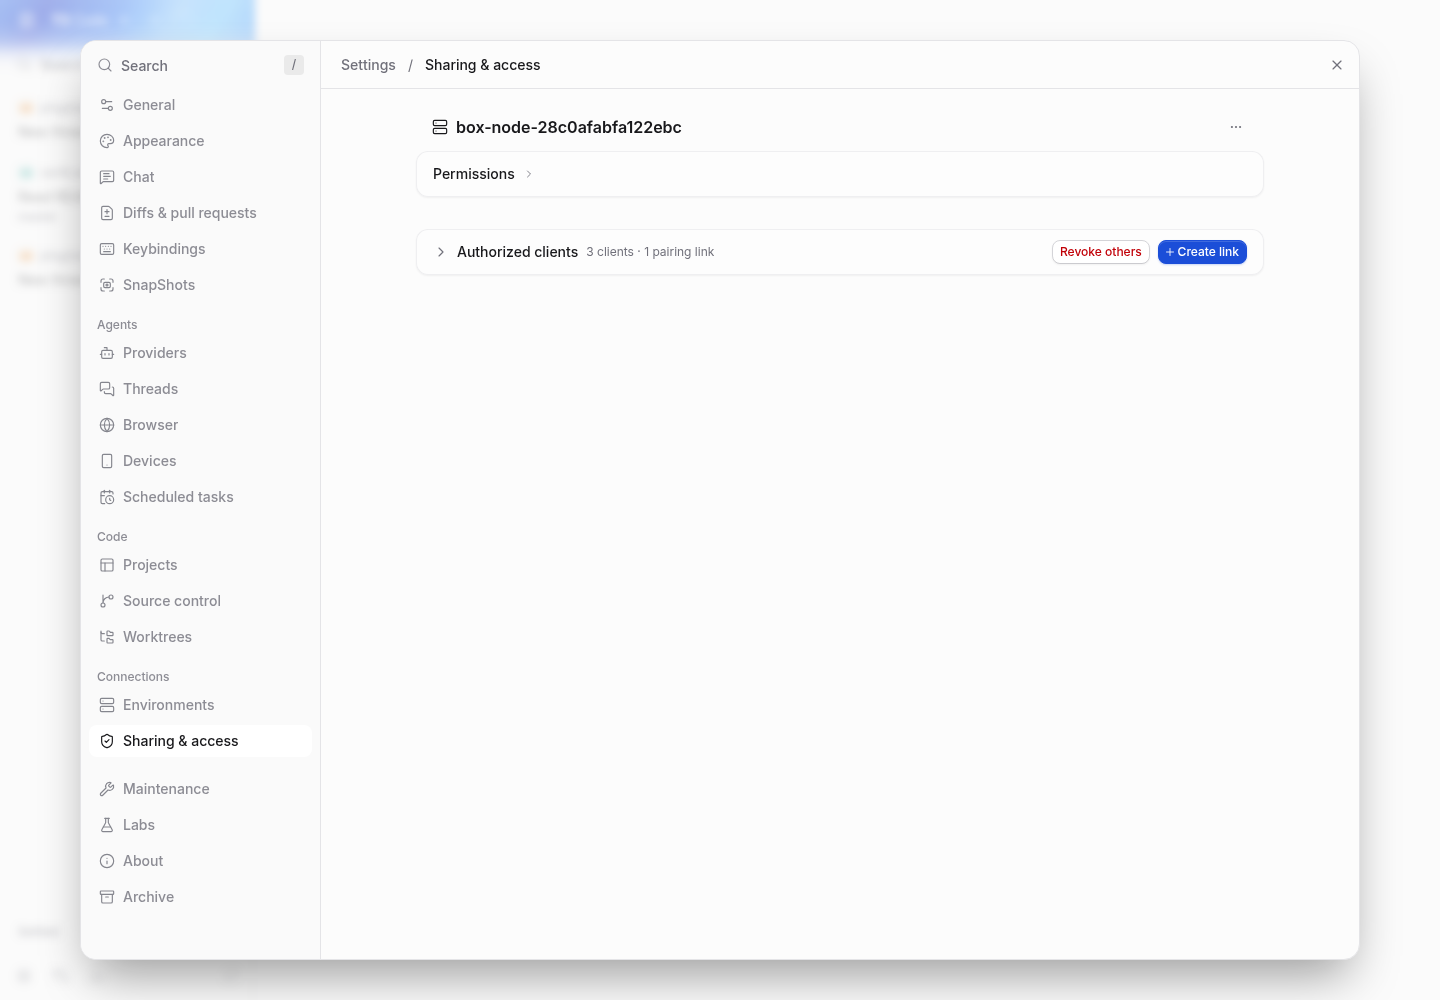
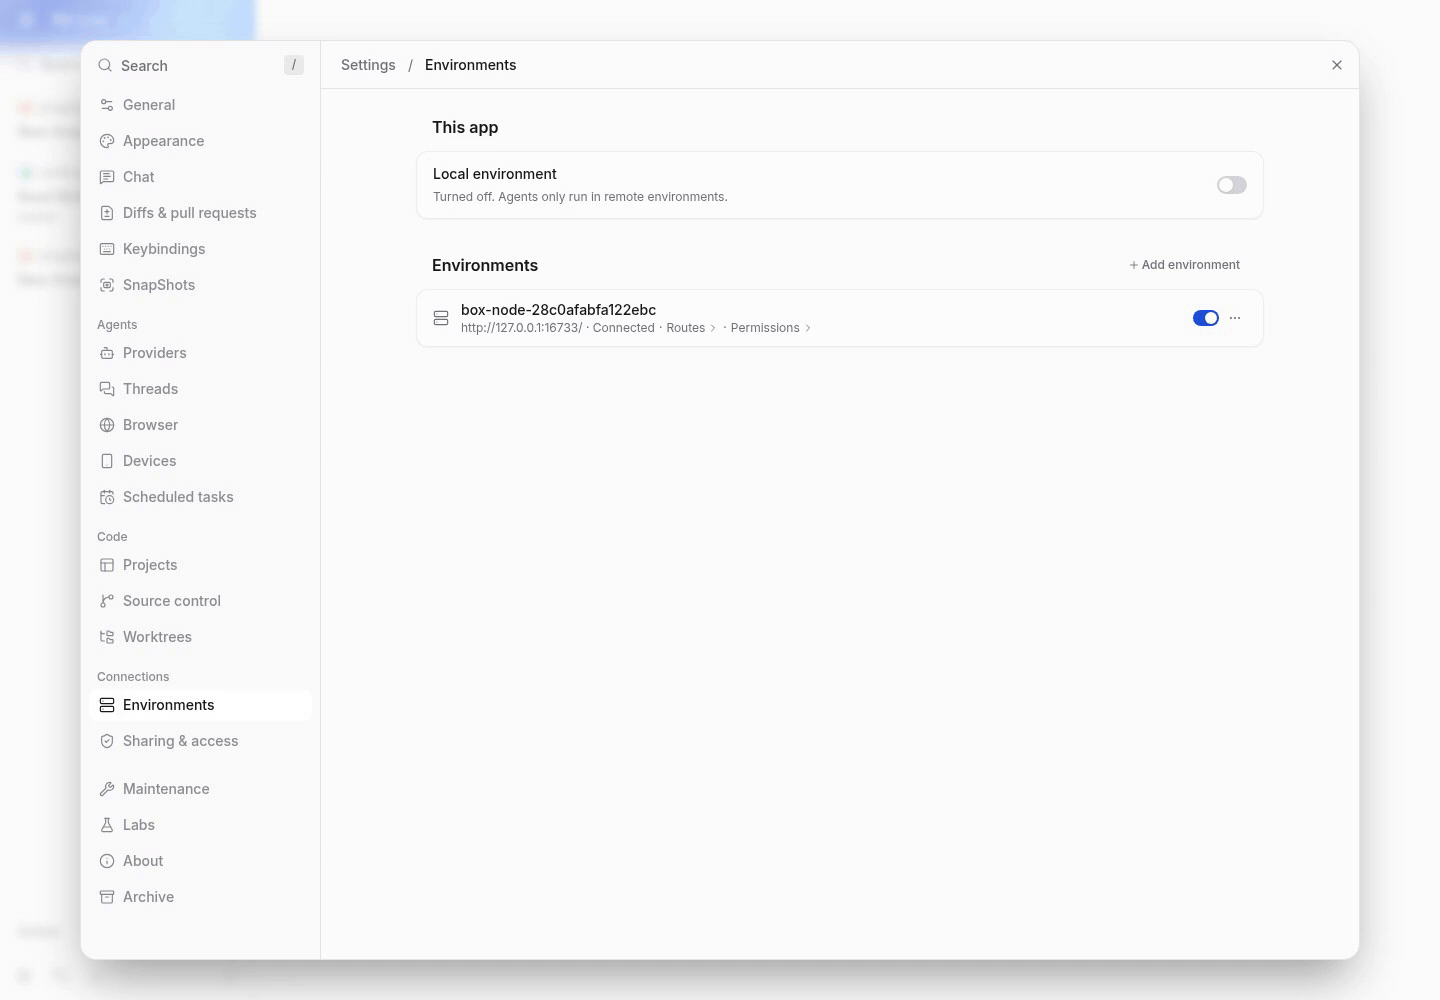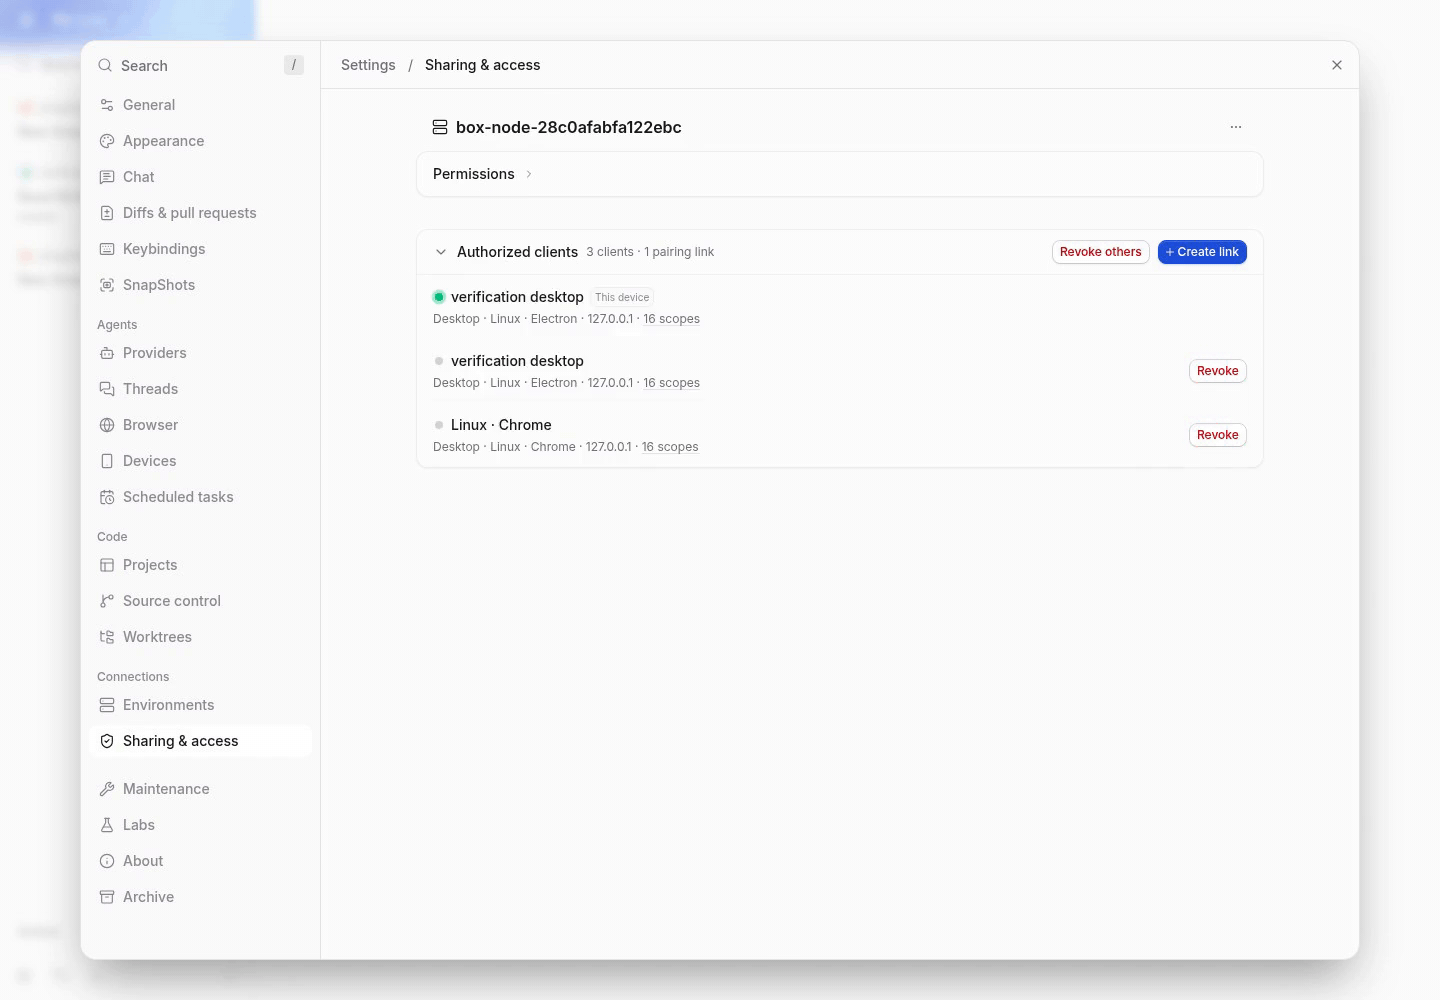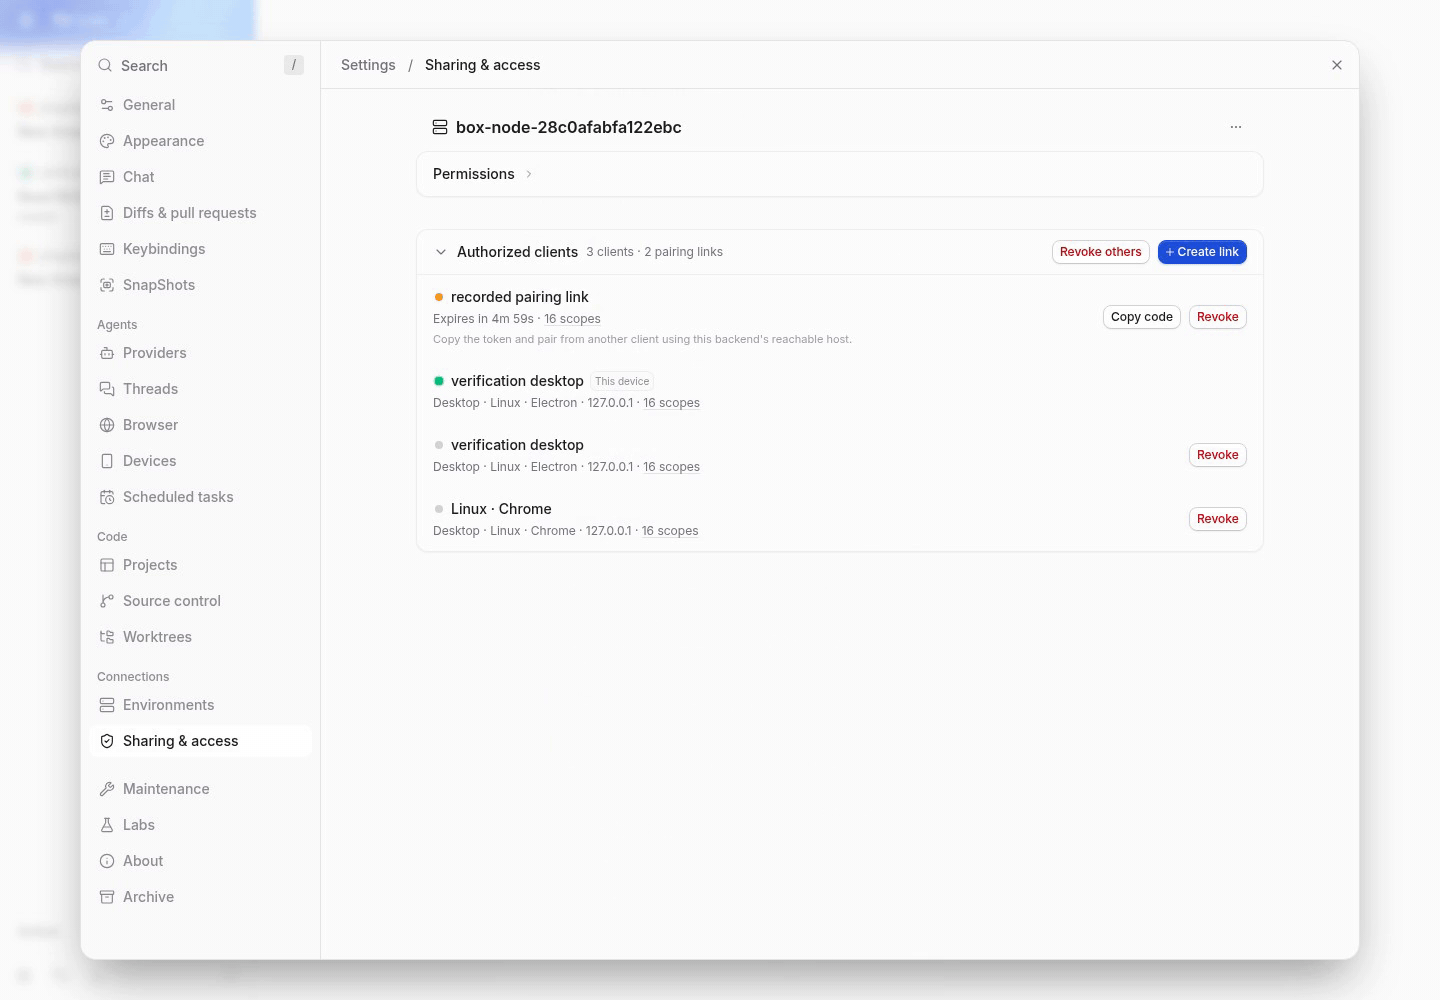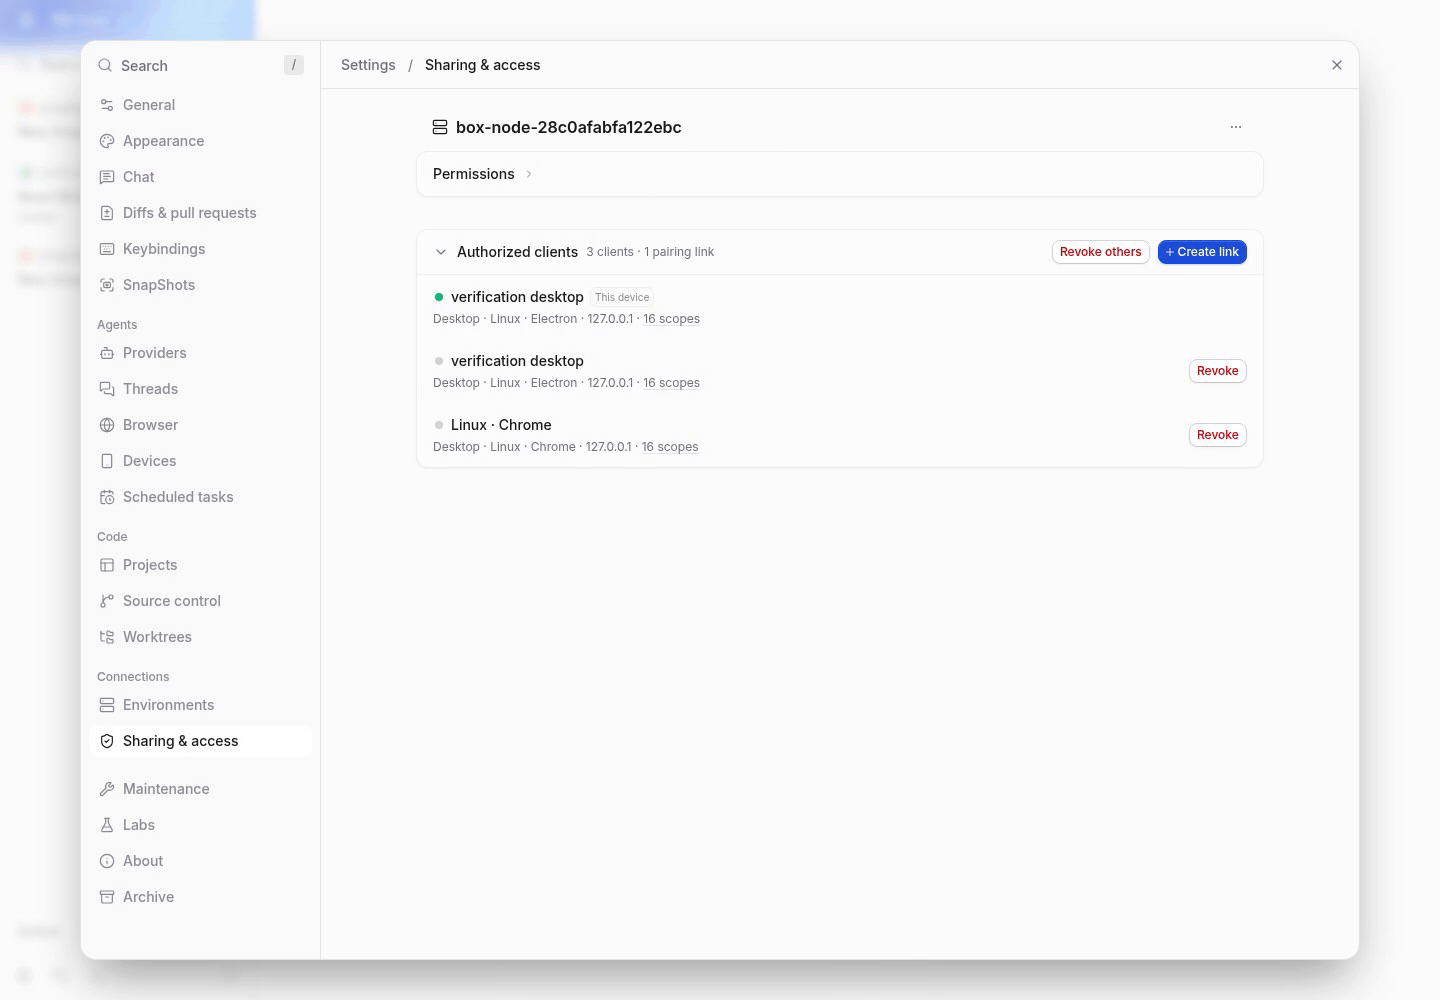
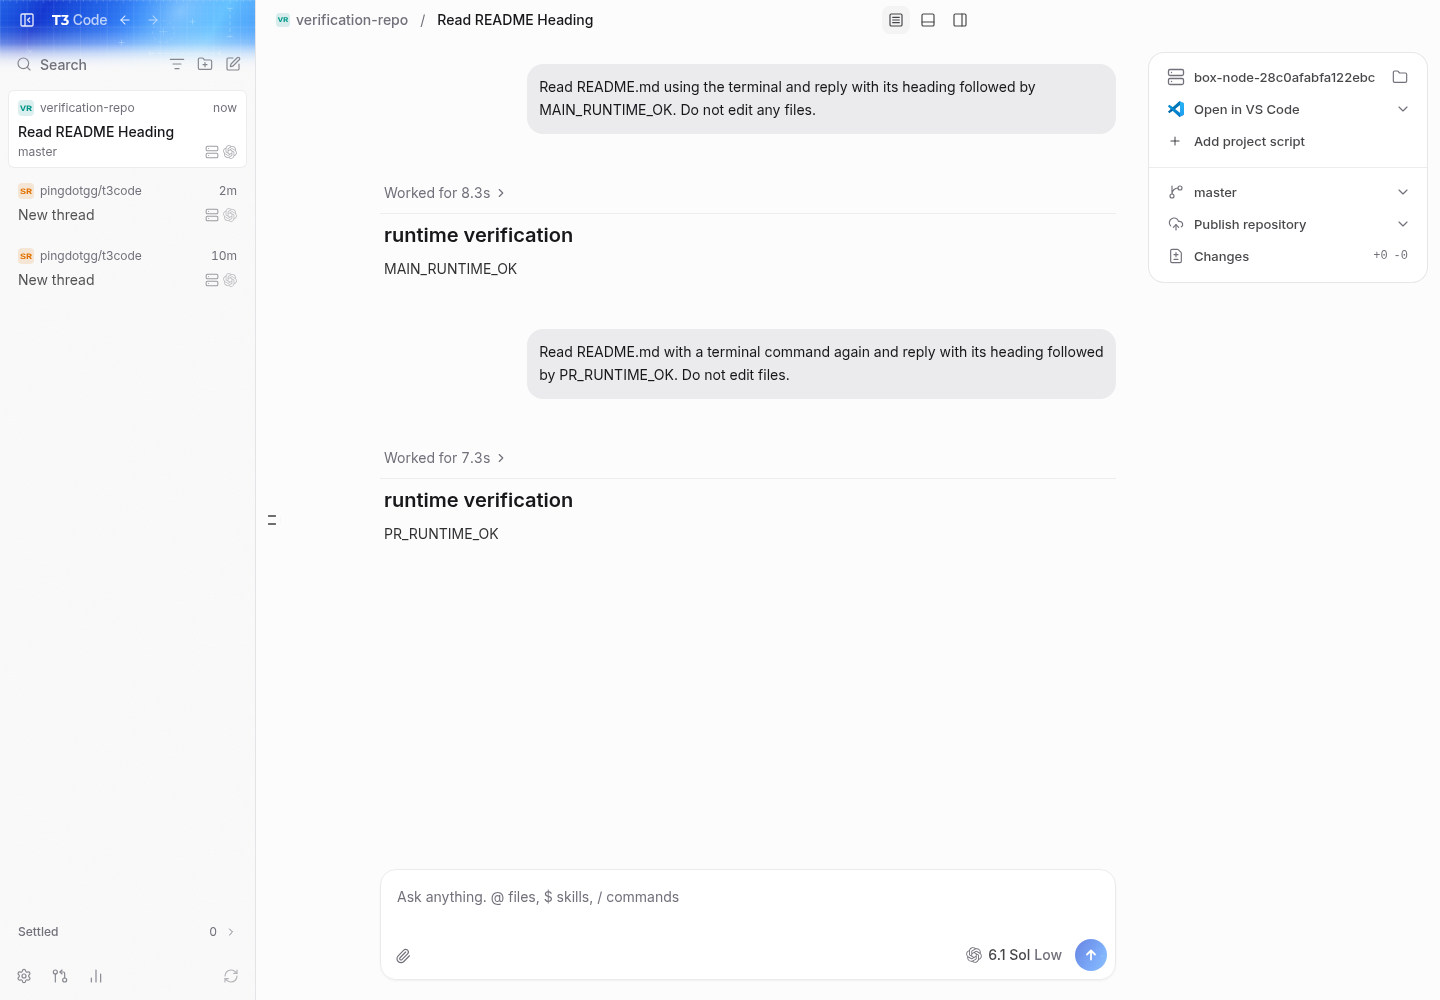



With Local environment off, the desktop app showed "No environment selected" in Sharing & access even while connected to a background service. The page now selects a connected service and offers a picker when several are available. Pairing and T3 Connect actions use that service's credentials and permissions. Desktop network controls remain restricted to the backend the app manages, and switching services clears the displayed pairing credential.
Closes #26420
Evidence
Verified head
d86991209bf586bf1d152e6f1ae3590198f5750c, built from basea185dd924889cd7f925760431a9f29b973a35e2f. The rebase preserves main's new collapsed pairing-link preview. An independent Codex review found no findings.Before
Historical Linux desktop reproduction at
48a292364ab37574c67fb377b5227e5d281d9203: a connected saved service has no access target with Local environment off.linux-before.mp4
After at this head
Physical corex, Linux Electron 44.10.1, two real bundled servers on loopback ports 27731 and 27732 with separate test homes. Both services were enrolled through Add environment. Electron used the production
gnome_libsecretbackend with a task-isolated GNOME secret-service session collection. The saved connection catalog was encrypted; Electron's basic store was not used.The recording follows Labs to Sharing & access, creates A's pairing link while Authorized clients is collapsed, switches to B, creates and revokes B's link, then returns to A. A's link survives B's revocation and its copyable credential is cleared on switching. It then revokes A's link, links A and B for publishing, unlinks A while B remains linked, and finally unlinks B. The last view shows Local environment off and both services connected. Idle pauses are shortened and the fixture boundary is captioned.
linux-final-short.mp4
Only unavailable external boundaries were fixtures: Clerk FAPI/session responses and its account widget, plus a local HTTPS relay. The real Clerk SDK, production renderer/hooks/controllers, selected-service HTTP authentication, and real
/api/connecthandlers ran unchanged. The relay fixture verified real Ed25519 proofs before returning invented per-environment credentials. The fixture certificate required Electron's--ignore-certificate-errors.Cloud linking in the recording is publish-only. The managed T3 Connect switch is visible and stays off. After each action, authenticated reads of both real servers and hashes of their secret files confirmed the selected service changed and the other service did not. All five checkpoints passed.
The Browser panel also exercised primary-environment pairing creation and revocation at this head. The collapsed list displayed its new preview, then removed it on revocation.
Web and macOS/Windows desktop run the same
ConnectionsSettings,AuthorizedClientsSettings,useCloudLinkControllerandexecuteConnectedEnvironmentHttpRequestpaths exercised here. Native mobile has separate UI; no mobile call sites use the new pairing commands, and no native mobile UI changed.Real server proof and checks
Against the two current-head servers, commands verified manual and managed link-proof signatures and claims, exact loopback ports, unauthorized/wrong-port rejection, account-mismatch rejection without mutation, and relay-config persistence. After restarting both servers, exact secret bytes, 0600 modes, preferences and signing keys survived. A's bearer failed on B; unlinking A left B's state and files unchanged.
Boat job
j_kz4jyhrkvej3ewyhzgfyexited 0.vp run check:changedpassed format, lint, both knip passes, affected-package typechecks, all 67 focused tests in 8 files, and 15 selected React compiler cases.vp run build:desktoppassed. The focused run includes environment HTTP authentication, auth commands, saved-service credentials, cloud controller behavior, selection, pairing rows and scheduled-task compatibility.Commands and successful output as text
Ready check compared this head with live main
d51bc58f5e05123a416a3737ac4bce42d1d76b7c. The merge is clean. Main advanced after the build with #30389, which changes tool-output display and provider adapters. It does not touch access, pairing, authentication or cloud-link code; the current-head runtime evidence and checks still cover the final PR diff. Maria merged the base during verification. The resulting diff changes deployment tooling and dialog-title line height; access, auth, pairing and cloud operations are unchanged from the independently reviewed rebase. Tests, server proof and the client capture were rerun on the merged head. All required checks pass and no review threads are unresolved. Auto-merge is off and there is no merge queue entry.Unverified live path: production Clerk login, live relay provisioning/revocation, managed connector startup, tunnel reachability, and guest links through a live tunnel. No dedicated test account is available. These external paths are not claimed by the fixture proof. Initial linking retains the server's existing loopback-origin restriction.
Implemented and rebased by Claude Opus 5.5 in Claude Code. Investigated, tested and independently reviewed by GPT-6.1 Sol in Codex through T3 Code.